Discipline 01
Security
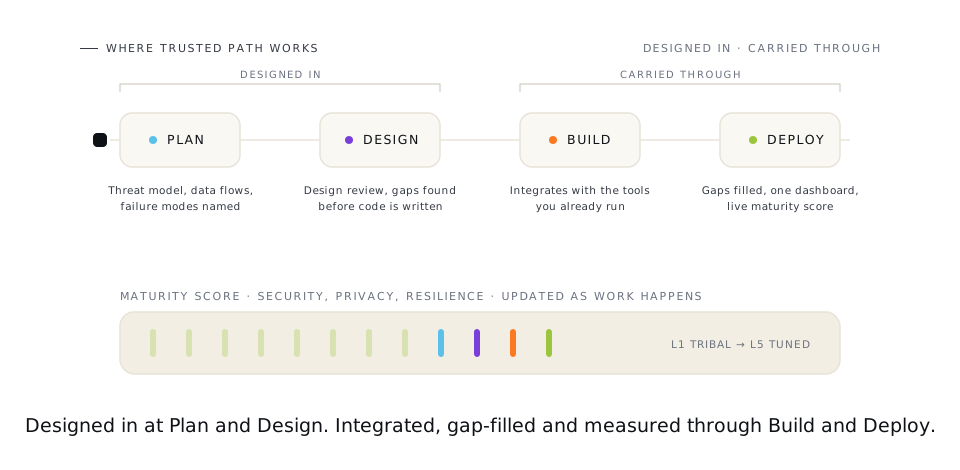
Threat modelling and secure design review at the planning stage, inside the tools and tickets engineers already use.
- Threat modelling from reusable patterns, before a line of code
- Control mapping to OWASP SAMM and NIST SSDF
- Findings written for engineers and fixed in the sprint